European Commission Targeted in AI-Enabled Cyberattack Disrupting Internal Systems
In November 2026, the European Commission experienced a cyberattack employing the AI tool ARTEX, causing ten days of internal system outages and raising concerns over employee data security.
AI News and Cybersecurity Insights
Part 1 of 1
Table of Contents
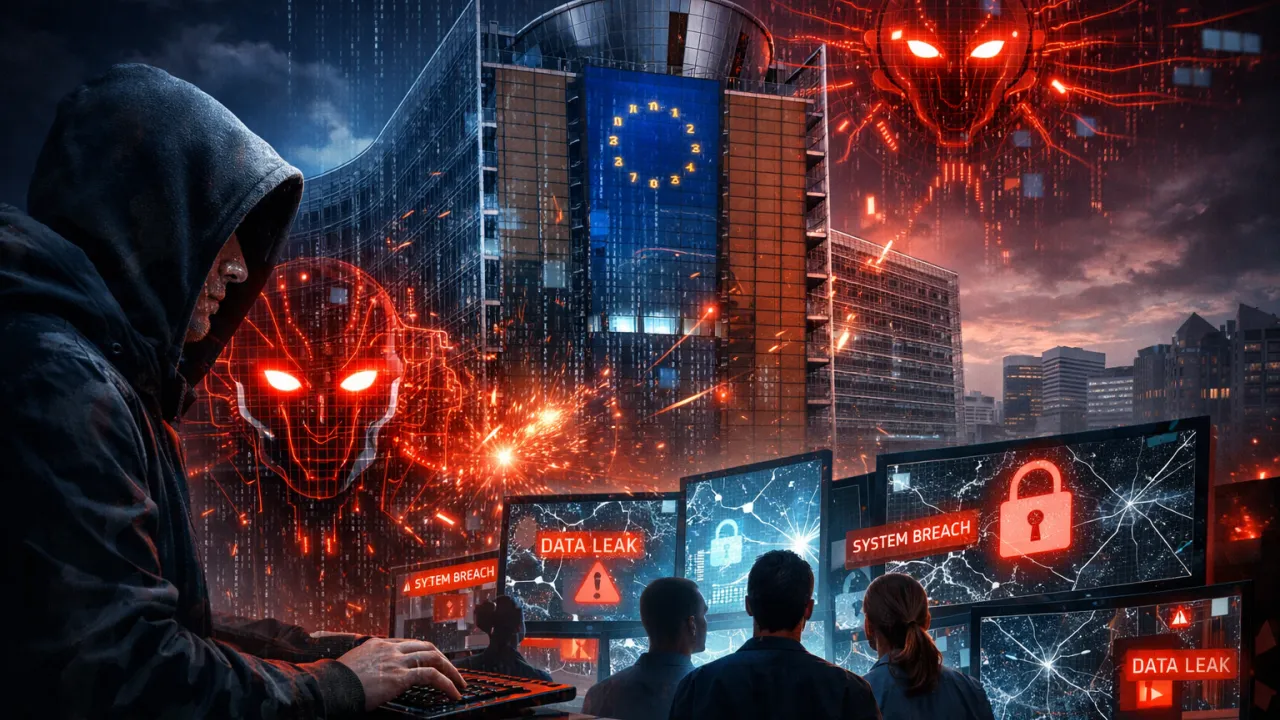
In early November 2026, the European Commission was the target of a significant cyberattack utilizing ARTEX, an artificial intelligence-based tool designed to identify system vulnerabilities and publicly available. This attack disrupted key internal systems—including the Sysper human resources platform, the MyPMO medical expenses reimbursement service, and translation services—resulting in operational outages lasting ten days.
The European Union’s cybersecurity agency, CERT-EU, detected the breach, prompting the Commission to temporarily shut down affected applications. While most systems have since been restored, investigations remain ongoing to determine whether attackers accessed employees’ personal data.
European Commission spokesperson Thomas Renier confirmed the incident and stated that appropriate security measures were promptly implemented. An emergency meeting of the Commission’s governing body was convened following the attack. Despite the disruptions, employee salaries were processed on schedule.
This incident highlights the evolving cybersecurity challenges posed by artificial intelligence, as AI tools are increasingly employed in both defensive and offensive cyber operations.
Related Posts